Framework’s Data Breach Exposed Customer Info: What You Need to Know
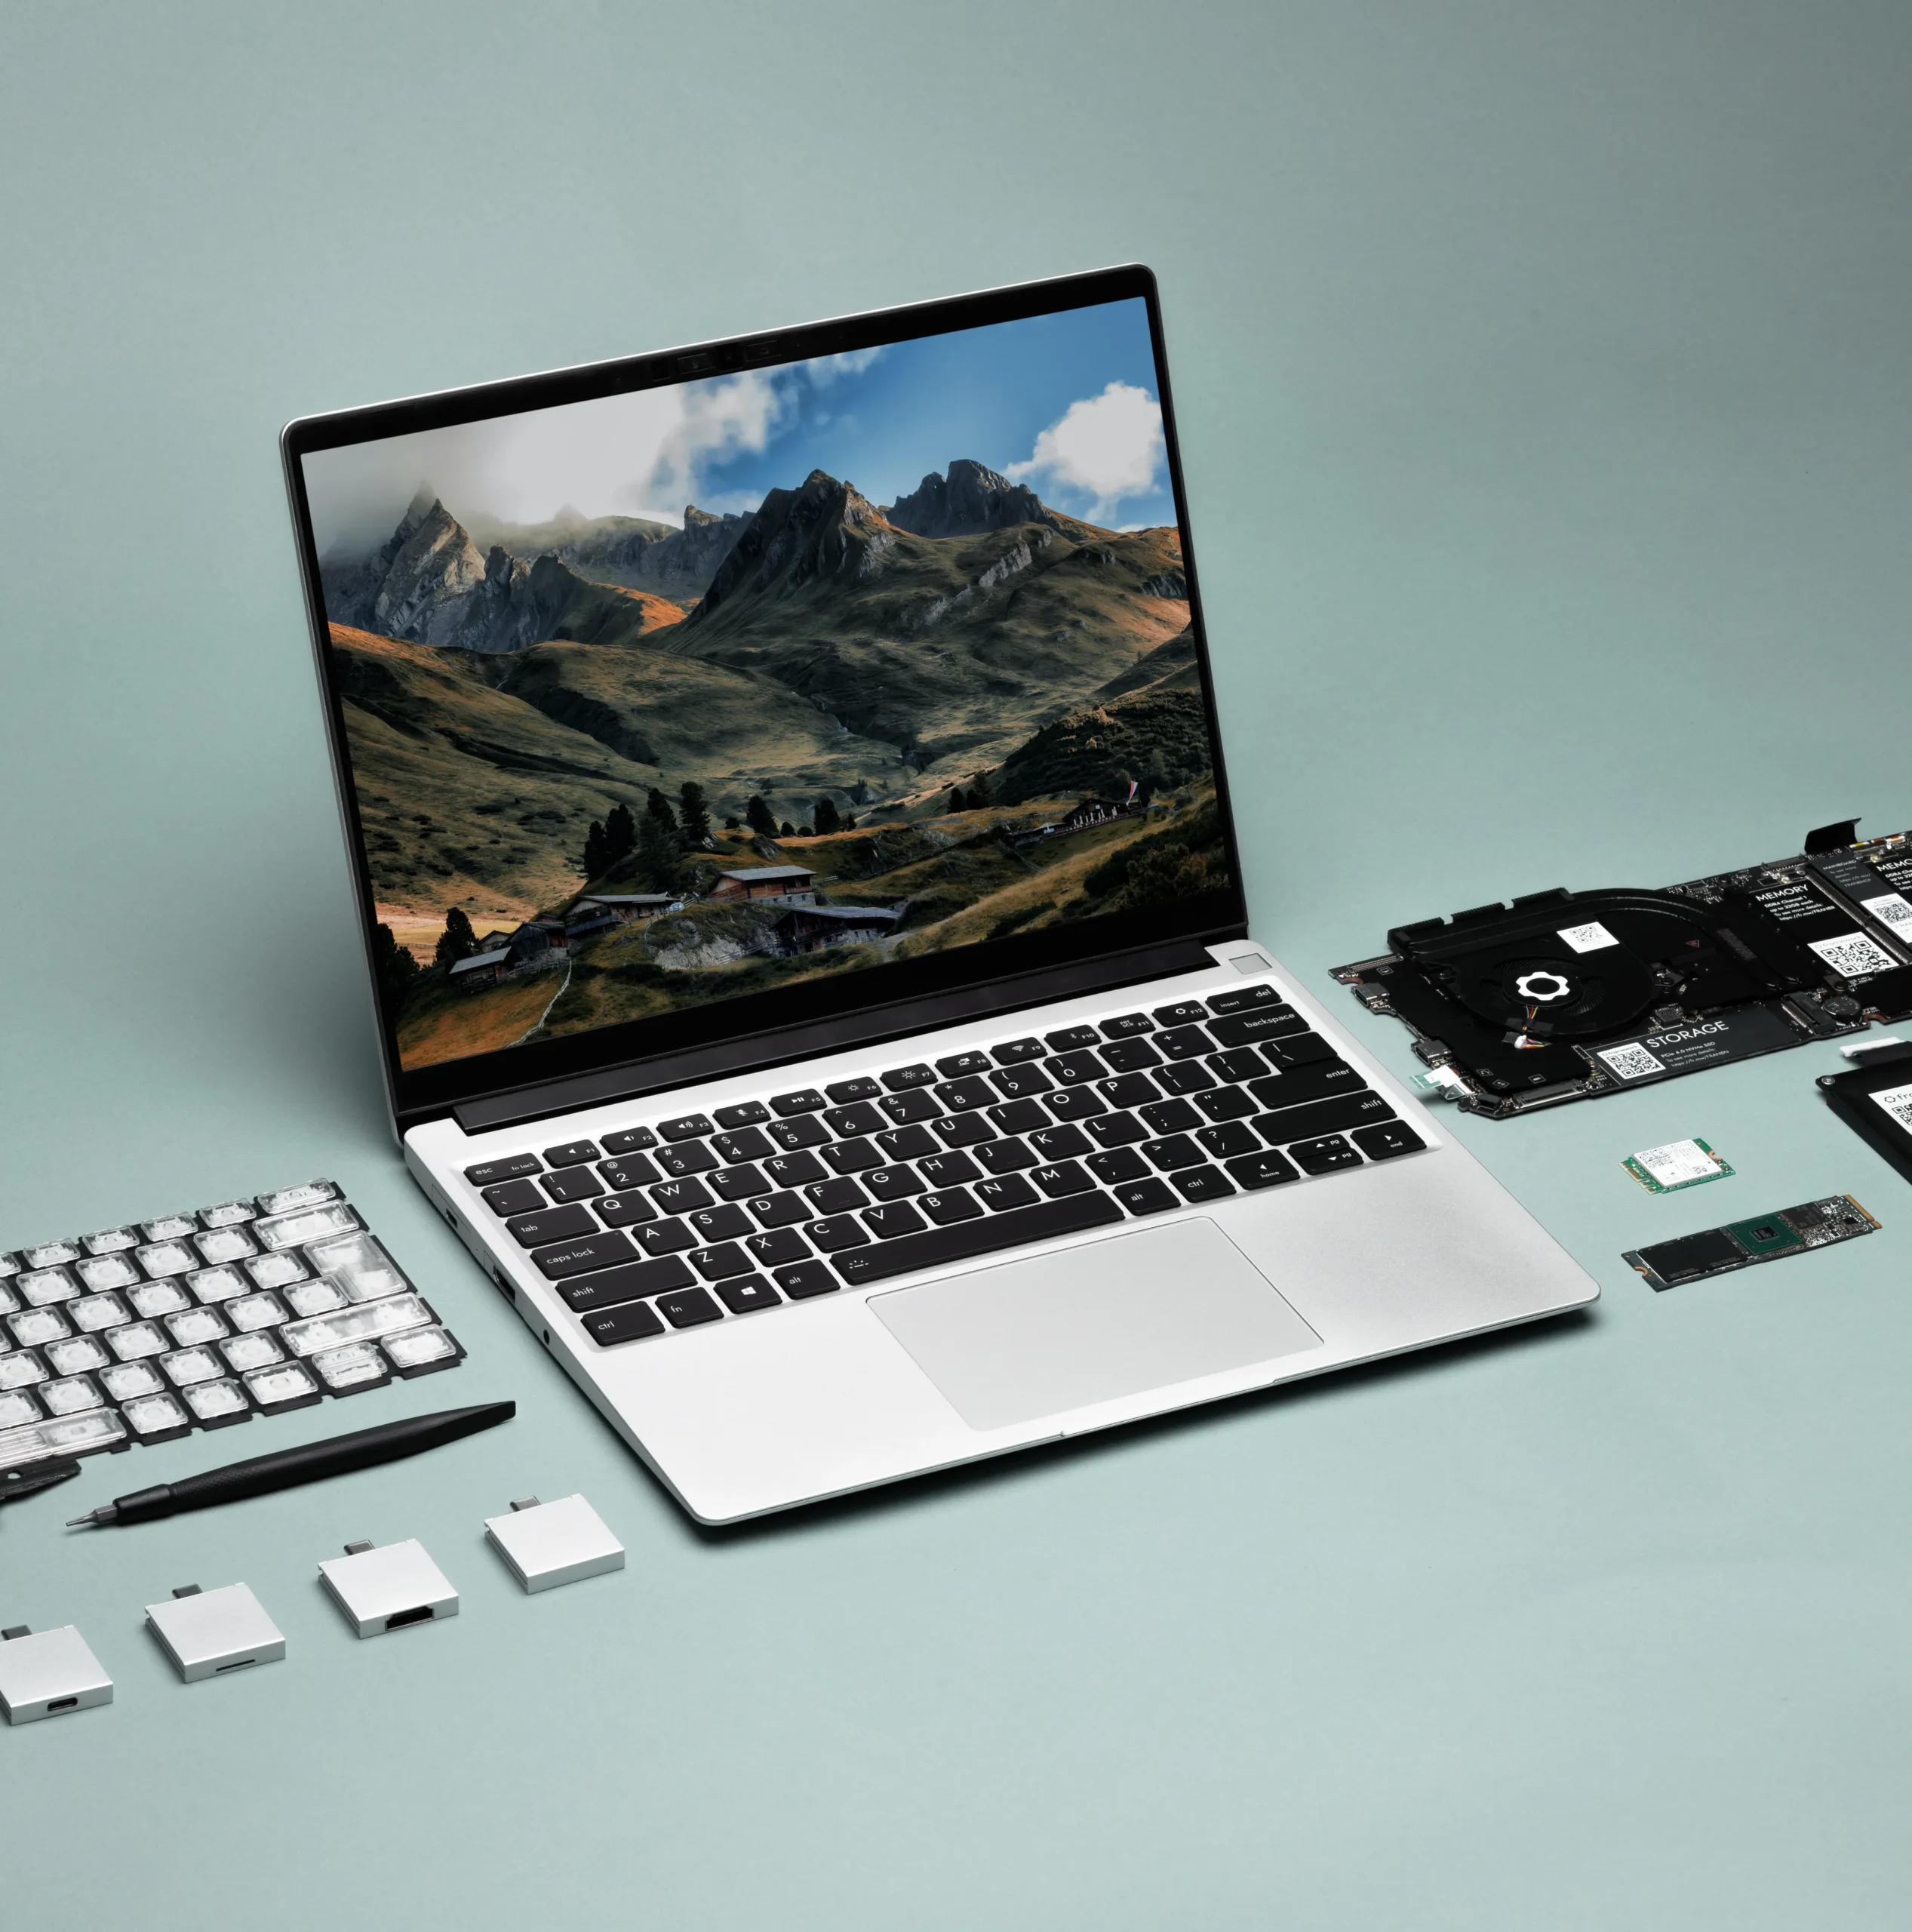
Framework, the company known for making modular, repairable laptops, just got hit with a data breach. And it’s bad.
Let me break down what happened, what was stolen, and what you should do if you’re a customer.
What Happened?
Framework suffered a significant data breach that compromised customer information. The company has been notifying customers via email.
According to TechCrunch, a Framework spokesperson confirmed that all customers were affected. They didn’t give an exact number, but estimates suggest hundreds of thousands of people are impacted.
A Framework representative didn’t immediately respond to a request for comment.
What Information Was Stolen?
Here’s what was accessed:
- Customer names
- Email addresses
- Phone numbers
- Login IPs
- Physical addresses
The good news: Framework says order and payment information wasn’t accessed in the breach. So your credit card details and purchase history should be safe.
How Did This Happen?
The breach appears to have been caused by a vulnerability in Metabase Cloud. Metabase is a business intelligence tool that companies use to analyze data.
The attackers used what’s called a “zero-day exploit.” That means it was a previously unknown security flaw that Metabase hadn’t patched yet.
In a blog post, Metabase said they’ve already patched the vulnerability. But they warned that companies hosting Metabase themselves might still be vulnerable. They recommend upgrading to the latest version.
The Timing Is Rough
Framework is already dealing with some serious challenges.
The company has been hit hard by the ongoing memory shortage. They’ve actually raised prices twice this year. The cost increase for memory modules was so significant that they had to reduce the RAM on the Framework Laptop 13 Pro, even though the product was already offered for preorder.
Now they have a data breach to deal with on top of that. Not great for consumer confidence.
What Should You Do If You’re Affected?
If you’re a Framework customer, here’s what you should do right now:
- Change your password — especially if you reuse passwords across sites
- Enable two-factor authentication — if you haven’t already, do it now
- Watch your payment cards — even though Framework says payment info wasn’t accessed, keep an eye on your statements
- Revoke access to services you no longer need or don’t recognize
- Be careful with phishing emails — scammers often use data breach news to send fake emails
The Bigger Picture
This isn’t an isolated incident. Data breaches are becoming increasingly widespread and severe across the industry.
CNET has reported that companies are often providing less transparency about the scope of compromised information and how attackers got in. So even when a company tells you about a breach, you might not get the full story.
Framework seems to be handling this one relatively transparently. They’re notifying customers directly and providing some details about what happened. But the fact that all customers were affected is concerning.
The Bottom Line
Framework got breached. Customer names, emails, phone numbers, IPs, and physical addresses were stolen. Payment info appears to be safe. The breach came from a Metabase Cloud vulnerability that has since been patched.
If you’re a Framework customer, change your passwords, enable two-factor authentication, and watch for phishing attempts.
It’s another reminder that no company is immune to data breaches. Not even the ones that build repairable, customizable laptops.